
Interfacing

DTO for Risk and Controls: Connect Risk to Execution

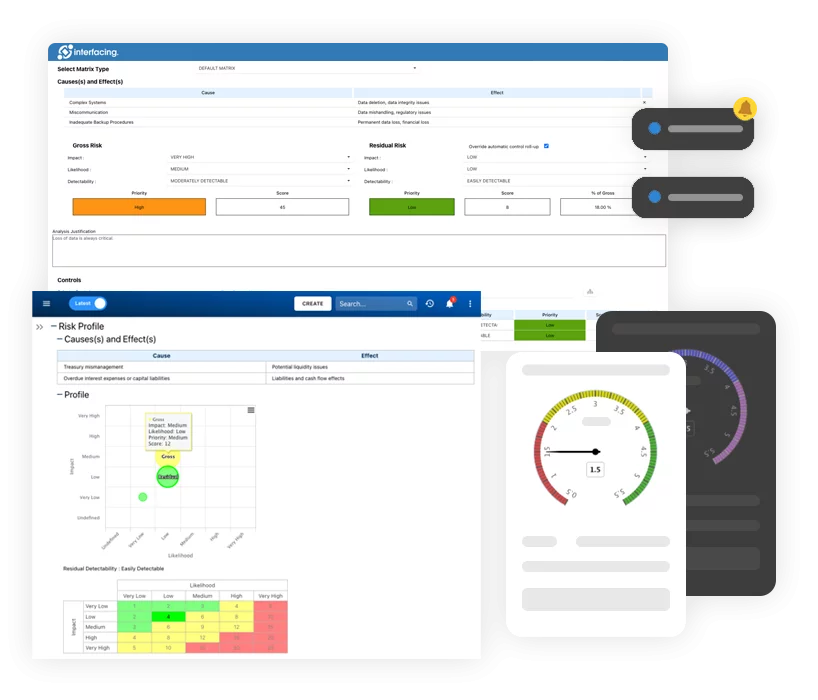
A DTO for Risk and Controls connects risks, controls, processes, systems and evidence in one operating model, helping organizations understand exposure, control effectiveness and change impact. AI-assisted analysis helps identify dependencies, emerging patterns and potential risk impacts across the organization. This gives leaders stronger context for decision-making while keeping human oversight, accountability and approval in […]

DTO for Compliance: From Requirements to Evidence

Compliance rarely fails because an organization does not know that a regulation, standard, policy, or contractual obligation exists. The harder problem is proving how that obligation is actually implemented across the organization. A DTO for compliance changes that perspective. Instead of treating compliance as a collection of requirements, documents, and audit evidence, a Digital Twin […]

DTO for Documents & Records: From Document Control to Connected Operational Evidence

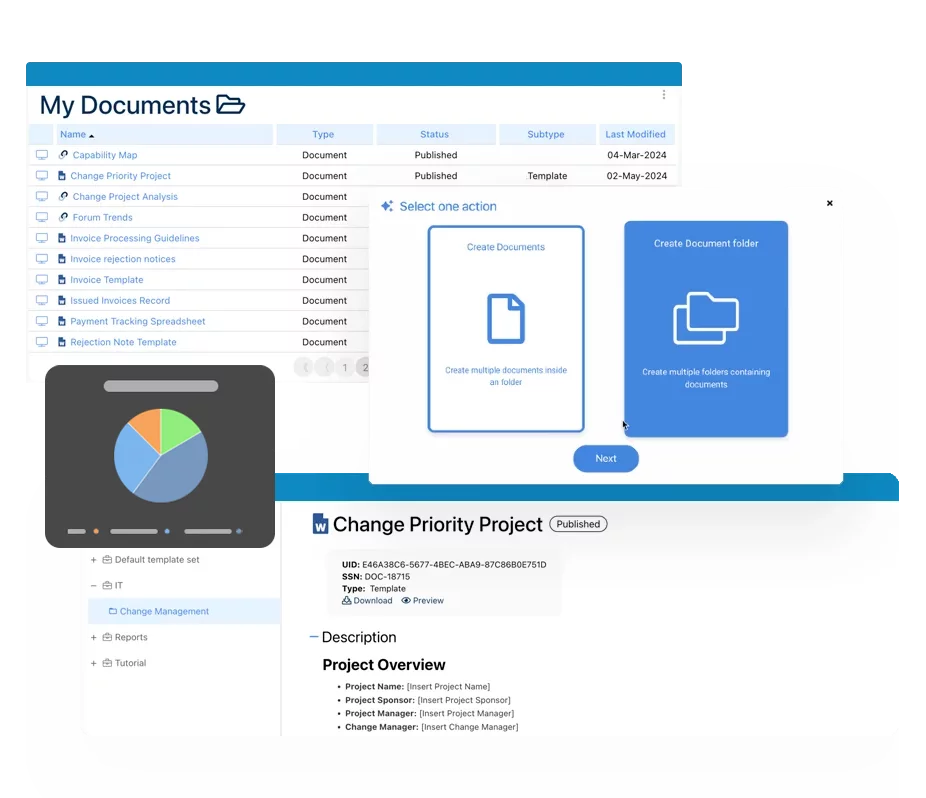
A Digital Twin of an Organization connects documents and records to the processes, roles, systems, risks, controls, regulations and training they support. Instead of treating information as isolated files, a DTO places it within the operating model so organizations can understand where it applies, what may be affected when it changes, and how records provide […]

DTO for Regulatory Change Impact: Know What a New Rule Actually Changes

Regulatory change rarely affects only the regulation itself. A revised requirement can alter processes, controls, SOPs, responsibilities, systems, training, evidence, and risk exposure across the organization. The real compliance challenge is therefore not identifying that a regulation changed. It is determining everything inside the organization that the change affects, deciding what must be updated, and […]

DTO for GRC: Connecting Governance, Risk and Compliance to the Operating Model

Governance, risk and compliance programs are designed to help organizations understand obligations, manage uncertainty and maintain control. Yet the information supporting those programs is often spread across risk registers, control libraries, policy repositories, audit systems, spreadsheets, process documentation and separate compliance applications. A Digital Twin of an Organization changes the structure behind GRC. Instead of […]

Digital Twin for Risk Management: From Risk Registers to Operational Risk Intelligence

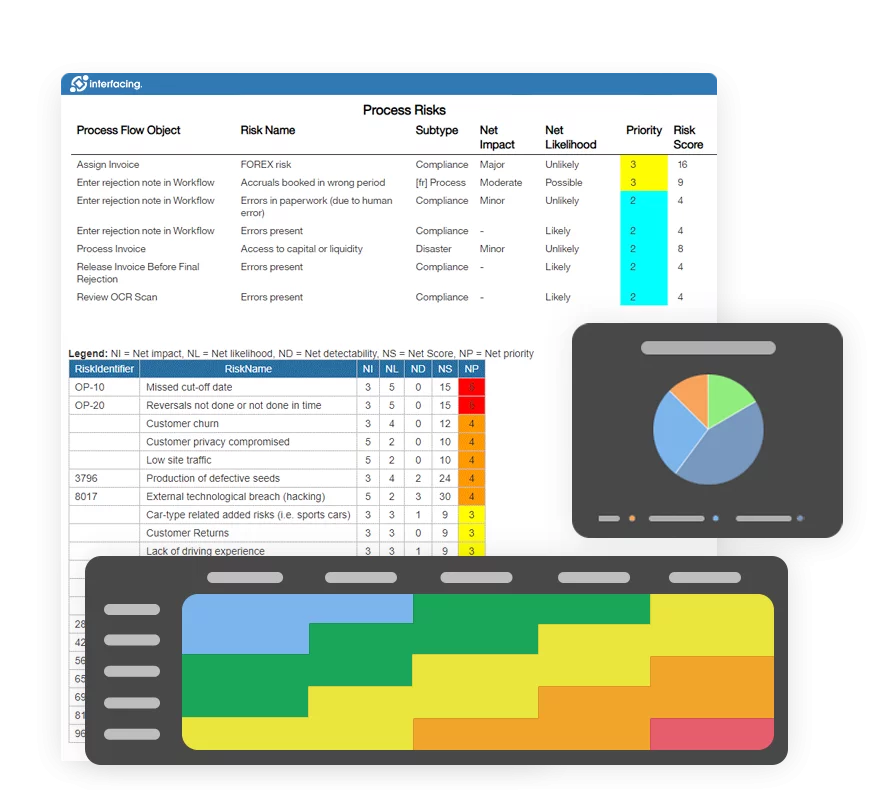
Risk management becomes difficult when risk is documented separately from the operations that create it. A Digital Twin of an Organization changes that relationship. Instead of viewing risks as isolated entries in a register, organizations can connect risk to processes, controls, systems, roles, suppliers, performance measures and operational dependencies. The result is not simply better […]

Why AI Agents Need More Than Process Context

Enterprise AI is quickly moving beyond answering questions and summarizing documents. AI-enabled agents are increasingly being considered for work that touches processes, systems, decisions and operational workflows. That makes access to information only the beginning of the problem. The harder question is whether an AI agent has enough organizational context to recognize not only how […]

Your AI Agents Know What to Do. But Do They Know What They’re Allowed to Do?

AI agents are moving beyond answering questions. They can interpret information, use enterprise tools, initiate workflows and increasingly participate in operational decisions. That changes the governance challenge considerably. The issue is no longer simply whether an AI agent can perform an activity. The more important question is whether the organization has explicitly determined which activities […]

An Approved SOP Is Not Necessarily an Accurate SOP

An approved SOP can still become operationally inaccurate after it has passed review and approval. Roles change, systems are replaced, controls are modified, regulations evolve, and processes are improved, often long before the procedure reaches its next scheduled review. Effective SOP governance therefore requires more than version control, it requires visibility into the operational relationships […]

Your Digital Twin Is Blind to Change If It Cannot Model Dependencies

Organizations rarely struggle because they cannot identify what changed. They struggle because they cannot see everything that the change will affect. A Digital Twin of an Organization becomes valuable when it reveals how processes, systems, people, policies, risks, controls, suppliers, data, and performance measures depend on one another. Without those relationships, the twin may document […]